A Practical Guide to Business Email Compromise Protection
Learn how to reduce business email compromise risk with practical safeguards, staff habits, and response steps that fit real teams.
Published on · Craig Wheeler · How this article was made
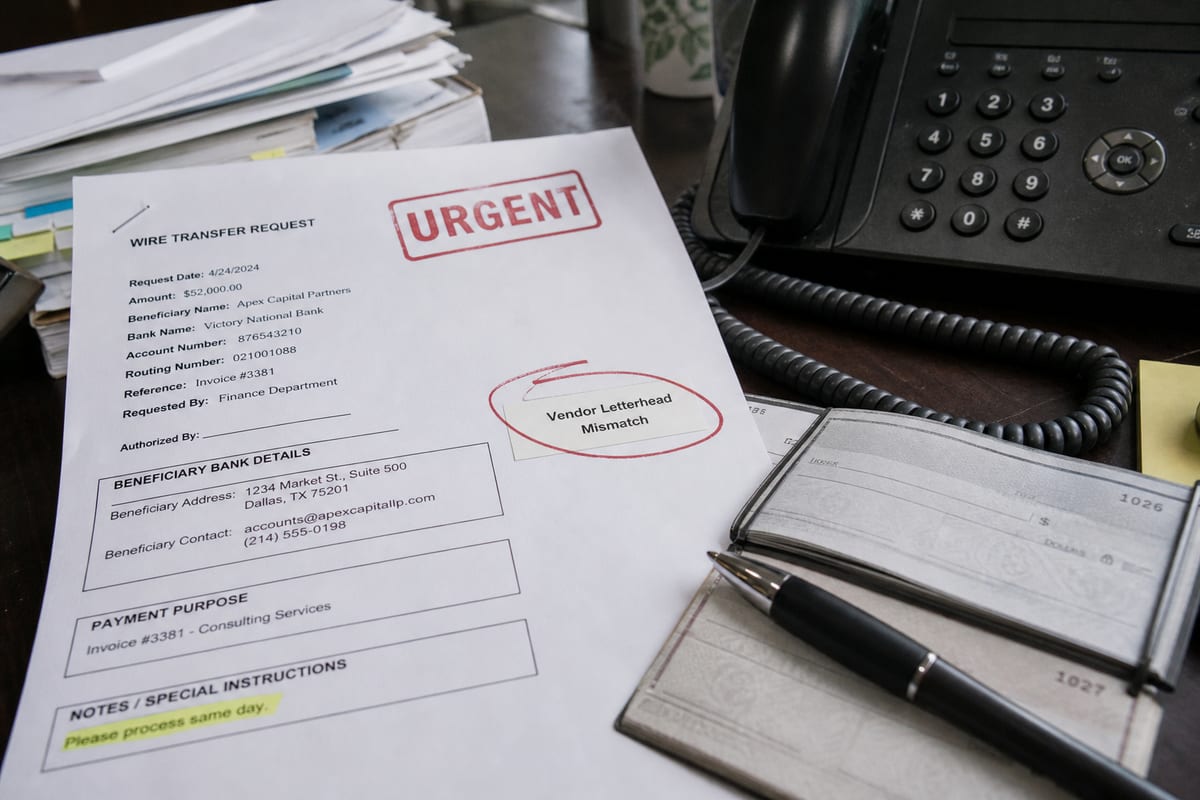
Business email compromise is one of the most costly and frustrating cyber threats because it does not always look technical. In many cases, it looks like a normal message from an executive, a vendor, a coworker, or a client. The goal is simple: get someone to send money, share sensitive data, or hand over access.
For small and midsize businesses, this risk is especially difficult because the attack often slips past people, not just software. Good protection comes from a mix of secure email settings, clear internal processes, and employee habits that hold up under pressure.
Why does business email compromise keep working?
Because it targets trust, urgency, and routine.
A criminal does not need to break every security control if they can convince one employee to act quickly. They may impersonate a company leader and ask for a wire transfer before a meeting. They may pose as a vendor and request a bank account change. They may send a fake Microsoft 365 login page to capture credentials and then use the real account to continue the scam from inside the mailbox.
These attacks work when the message feels familiar enough that nobody pauses to verify it.
Which businesses are most at risk?
Any business that uses email to approve payments, exchange documents, reset passwords, or communicate with vendors is a potential target.
That includes law firms, healthcare offices, construction companies, nonprofits, manufacturers, property managers, and professional services firms. Smaller organizations are not too small to be noticed. In fact, they are often attractive targets because approval workflows are less formal, teams are busy, and one person may wear several hats.
The first question to ask, what are attackers trying to get?
Most business email compromise attempts aim for one of four outcomes:
- Fraudulent payments, such as wire transfers or gift card purchases
- Payroll diversion, where direct deposit details are changed
- Sensitive data, such as tax records, contracts, or customer information
- Account access, usually by stealing Microsoft 365 credentials
Understanding the end goal helps you build better defenses. If your finance team can spot payment fraud but HR has no process for verifying payroll changes, you still have a gap.
How can you tell the difference between phishing and business email compromise?
Phishing is a broad category. Business email compromise is a more targeted form of fraud that often uses impersonation and social engineering tied to real business activity.
A generic phishing email might claim your mailbox is full and ask you to log in. A business email compromise attempt might reference an actual invoice, a real executive name, or an ongoing project. It may come from a lookalike domain, a compromised vendor account, or even a genuine internal mailbox that has already been taken over.
That is why protection has to go beyond spam filtering.
Common warning signs your team should know
Some attacks are polished, but many still leave clues. Teach employees to slow down and look for patterns like these:
- A sudden request to bypass normal approval steps
- Pressure to act immediately or keep the request confidential
- A reply asking to change banking details or payment instructions
- Slight misspellings in a sender domain
- Unexpected document sharing requests or login prompts
- Messages sent at odd times that do not match the sender’s normal style
A short list like this is useful, but it works best when paired with practice. Teams need examples that match the kinds of requests they handle every day.
Is multi-factor authentication enough?
It is essential, but it is not enough by itself.
Multi-factor authentication can stop many account takeover attempts, especially when a password has been stolen. But attackers also use session hijacking, MFA fatigue prompts, and social engineering to get around weak implementations. If someone approves a fake login request or enters a code into a fraudulent site, the protection can fail.
Strong business email compromise protection usually includes MFA, conditional access policies, mailbox auditing, alerting, and user training. If your organization relies heavily on Microsoft 365, it also helps to review your broader cloud security posture and access controls. For teams exploring where automation and security overlap, AI for business services can also support smarter monitoring and workflow checks when used carefully.
Which technical controls make the biggest difference?
Start with the basics that reduce impersonation and account abuse:
- Enforce multi-factor authentication for every mailbox, especially executives, finance, and administrators
- Use SPF, DKIM, and DMARC to help prevent domain spoofing
- Block legacy authentication where possible
- Review forwarding rules and alert on suspicious mailbox changes
- Limit admin privileges and separate admin accounts from daily email use
- Turn on mailbox auditing and sign-in alerts
- Use conditional access policies for risky logins, locations, and devices
These controls do not replace people and process, but they make attacks harder to pull off and easier to detect early.
Why do payment verification procedures matter so much?
Because many business email compromise incidents succeed at the exact moment a person decides to trust an email instruction.
Your team should never change payment details, approve a wire, or buy gift cards based only on an email request. Build a simple verification process that uses a second channel, such as a phone call to a known number, not the number listed in the suspicious message. The process should be documented, easy to follow, and consistent, even when the request appears to come from leadership.
This is where many businesses improve quickly. The technology may already be in place, but the approval workflow is still too informal.
Should small teams train everyone, or just finance and leadership?
Everyone should get baseline training, and higher-risk roles should get more specific guidance.
Executives, finance, HR, operations, and anyone with access to customer or vendor data need scenario-based training that reflects the real requests they receive. Reception, sales, and support staff also matter because they may be the first to see impersonation attempts or unusual requests.
Good training is not about fear. It is about giving people a repeatable way to pause, verify, and escalate concerns.
A useful question from readers, what should an employee do if a message feels off?
Give them a simple script:
- Do not click links, open attachments, or reply right away.
- Check the sender address carefully.
- Compare the request to normal process.
- Verify the request using a separate channel.
- Report it to IT or security.
The easier this process is to remember, the more likely your team will use it under pressure.
How do compromised vendor accounts change the risk?
They make attacks much more convincing.
If a criminal gains access to a real vendor mailbox, they can read existing conversations, learn invoice timing, and insert themselves into active threads. That can make the request look legitimate, even to experienced staff.
To reduce this risk, confirm payment changes through a known contact method, watch for subtle changes in writing style or instructions, and review email security with key vendors. This is also a good reason to strengthen logging and alerting around suspicious account behavior. Businesses that want earlier visibility into unusual activity often benefit from IT Monitoring Services.
Can email security tools stop this on their own?
No, and that is the point many teams miss.
Secure email gateways, anti-phishing tools, and Microsoft 365 protections are valuable. They can block spoofing, flag risky messages, and reduce noise. But business email compromise often succeeds through context, timing, and human decisions. A tool may identify some attacks, but it cannot fully replace verification procedures or judgment.
The best results come from layers: email security, identity protection, monitoring, clear approval workflows, and regular training.
When should a business worry that an account is already compromised?
Look for signs like these:
- Unexpected mailbox rules or forwarding settings
- Login alerts from unusual devices or locations
- Users reporting missing messages or strange sent items
- Vendor or customer complaints about odd replies
- MFA prompts the user did not initiate
- Payment or payroll changes that nobody can clearly explain
If you see even one of these, investigate quickly. Early containment can prevent a stolen credential from turning into wire fraud or data loss.
A practical response plan, what should you do after a suspected incident?
Move fast and keep the steps clear.
- Reset the affected account password
- Revoke active sessions
- Review MFA status and recent sign-ins
- Check inbox rules, forwarding, and delegated access
- Search for similar messages sent internally or externally
- Contact the bank immediately if money was sent
- Notify impacted vendors, customers, or staff as needed
- Preserve logs and message details for investigation
If the incident involved a spoofed domain, account takeover, or fraudulent payment request, document exactly what happened and where the process broke down. That review is often the fastest path to stronger protection.
Does AI help with business email compromise protection?
It can, when used in a focused way.
AI can help identify unusual communication patterns, support faster triage, and reduce manual review time. It can also assist with awareness training by generating realistic examples for different departments. But it still needs good data, sound policies, and human oversight.
If you are evaluating where AI fits into your security and operations strategy, this AI for business overview offers a practical starting point.
How often should you review your defenses?
At least quarterly for key controls, and immediately after staffing changes, vendor changes, or any suspicious event.
Review who has access to sensitive mailboxes, whether MFA is enforced, whether domain protections are configured correctly, and whether finance and HR procedures still match the way your team actually works. Test your process with realistic scenarios, not just policy documents.
A control that looked good on paper six months ago may not hold up today if your workflows changed.
The goal is not perfect email, it is safer decisions
Business email compromise protection is really about reducing the chance that one believable message turns into financial loss, exposed data, or a damaged relationship. The strongest defenses combine secure email and identity controls with simple verification habits that people can actually follow.
If your team is unsure where the biggest gaps are, start with the highest-risk workflows: payments, payroll, executive requests, vendor changes, and login security. Tightening those areas first usually gives you the most practical improvement.
If you want a clearer plan for protecting your organization, reach out to our team to learn how we can help with business email compromise protection.